
Bill Nelson
72 articles by Bill Nelson on the Identity Fusion blog
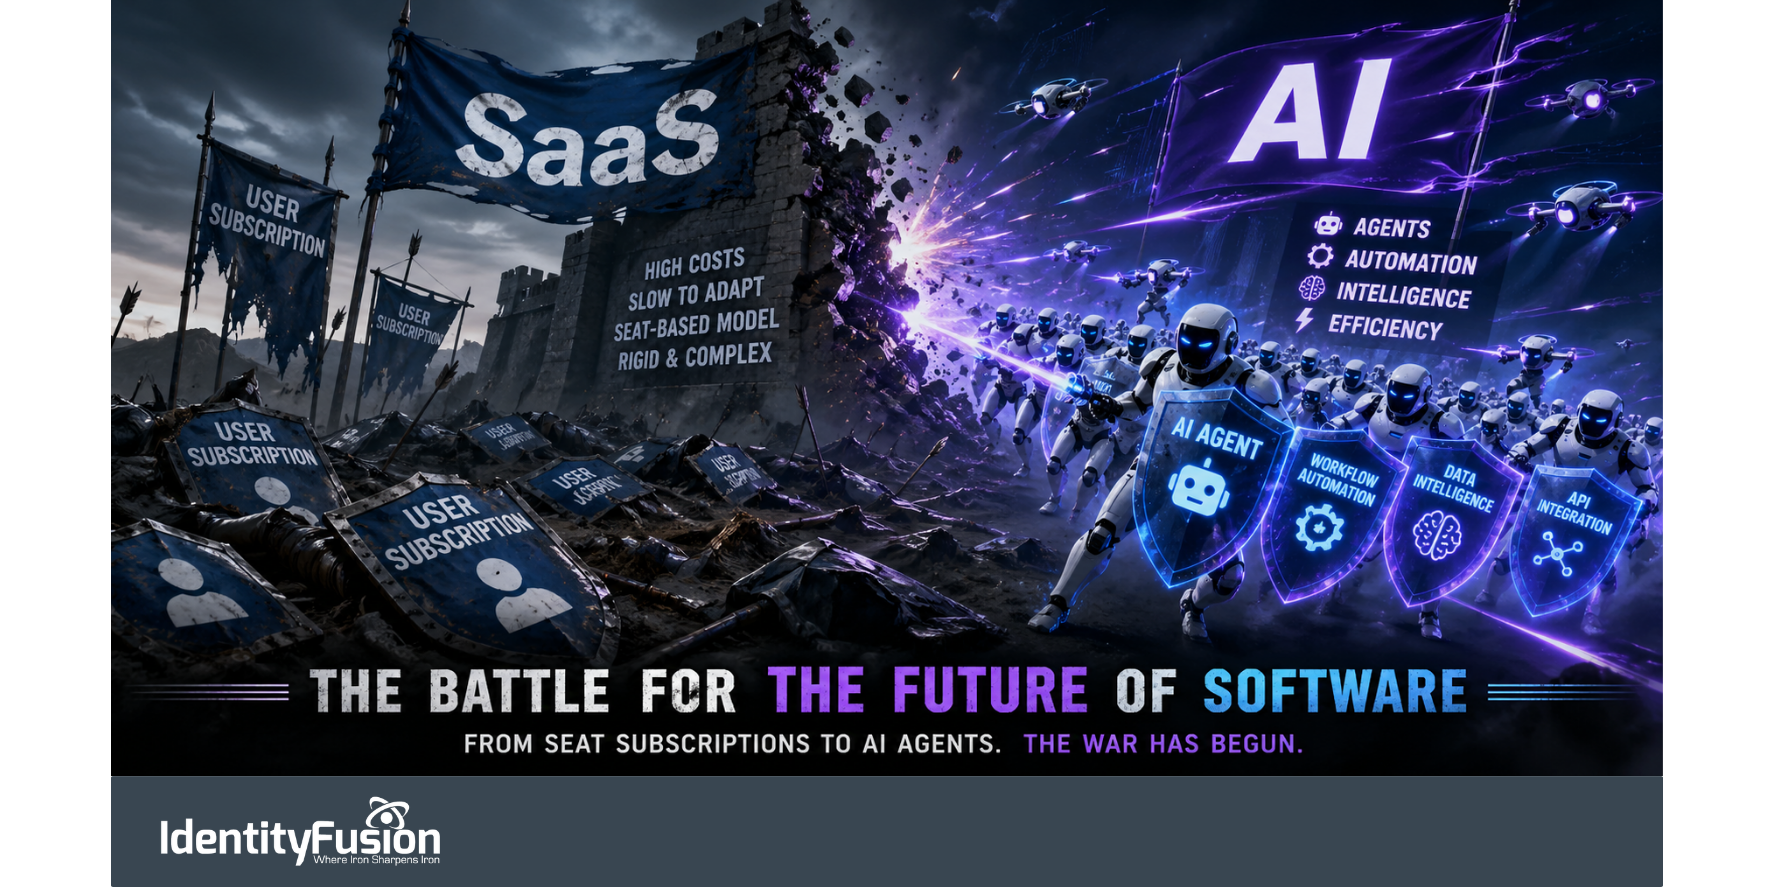
Killing SaaS in Order to Save It
Explore how AI is reshaping the SaaS landscape, challenging traditional models and prompting companies to rethink their software strategies for better outcomes.

Life in the Impact Zone: Surfin’ the Turbulent Waters
Navigating life's turbulent moments with resilience and support, inspired by the lessons of surfing and the wisdom of Duke Kahanamoku.

The Hidden Risk in Your Partner Network: Why B2B IAM Can’t Be Ignored
Discover how B2B IAM solutions streamline partner onboarding, enhance security, and improve operational efficiency for organizations managing external business relationships.

Measure Twice, Cut Once
Discover the timeless wisdom of "measure twice, cut once" and its crucial application in identity and access management for secure and efficient project execution.

The Strategic Value of Failing Early
Learn how failing early in software development uncovers issues when they're easiest to fix, fostering resilience and innovation in your tech team.

The Myth Behind Modern IGA Deployments
Transform Identity Governance and Administration (IGA) from a mere IT project into a strategic business enabler with our expert insights. Discover why strategy and alignment are crucial for successful IGA programs.

Migrating to an Identity Cloud: What the Vendors Won’t Tell You
Discover the key considerations, hidden complexities, and crucial questions to ask before migrating your on-premise IAM solution to a cloud-based identity platform.

Identity Fusion Announces Strategic Partnership with Dock Labs to Bridge the Gap Between Legacy IAM and Next-Generation Identity Solutions
Discover how Identity Fusion's partnership with Dock.io enhances IAM with decentralized identity solutions, streamlining verification, and future-proofing security for modern enterprises.

Future-Proofing Identity: Bridging the Gap to Identity 3.0
Learn how to transition to Identity 3.0 by modernizing your IAM strategy with Zero Trust, AI, automation, and decentralized identity principles.

The State of Identity 3.0: Where Are We Now?
Discover the rise of Identity 3.0, its current adoption, key players, and the path to mainstream digital identity transformation.

New Year, New Beginnings: Embracing the Future of Identity and Access Management in 2025
Discover how Identity 3.0 technologies like verifiable credentials, self-sovereign identity, and identity wallets are redefining security and privacy in 2025.

Identity 2.0 vs Identity 3.0: A Comparative Analysis
Discover how Identity 3.0 revolutionizes digital identity management with enhanced security, privacy, and user control, moving beyond the limitations of Identity 2.0 systems.

The Road to Identity 3.0: Challenges Associated with Implementing a New Identity Paradigm
Discover the challenges and solutions to implementing Identity 3.0, a revolution in digital identity that promises security, privacy, and user control over personal data.

The Ghost of Identity Yet to Come
Explore the future of digital identity, contrasting centralized control with empowering decentralized systems, and learn how our choices today shape tomorrow's identity landscape.

The Ghost of Identity Present: Exploring Modern Identity Solutions
Explore the evolution of modern identity solutions, highlighting advancements, challenges, and the future of self-sovereign identity in our digital world.

The Ghost of Identity Past: A Reflection on Historical Identity Solutions
Explore the evolution of identity management, from paper-based credentials and passwords to modern, secure, and user-friendly systems, learning from the past to build a better future.

The Evolution of Identity: Past Lessons, Present Innovations, and Future Possibilities
Explore the evolution of identity management solutions from past challenges to future innovations, drawing insights from 'A Christmas Carol' to build secure digital systems.

Welcome to Identity 3.0: A Revolution in Digital Identity
Discover Identity 3.0: a revolutionary approach to digital identity that enhances privacy, security, and user empowerment through verifiable credentials, digital wallets, and self-sovereign identity.

Empowering User Authorization with Verifiable Credentials
Discover how Verifiable Credentials (VCs) are transforming secure and efficient user access in healthcare, finance, and workforce management, enhancing security and compliance.

Revolutionizing Authentication with Verifiable Credentials: Use Cases Across Industries
Discover how verifiable credentials are revolutionizing authentication across healthcare, finance, and workforce management, ensuring security, privacy, and efficiency in digital identity verification.

How Verifiable Credentials are Killing Fraud and Slashing Dropouts During User Onboarding
Learn how verifiable credentials enhance security, reduce fraud, and streamline user onboarding processes across various industries.

Digital Identity Wallets: What’s Holding Us Back?
Discover how digital identity wallets can revolutionize online interactions by enhancing privacy, security, and convenience, while addressing key challenges for widespread adoption.

Your New Digital ID: How Identity Wallets Are Redefining Trust in the Digital Age
Discover how digital identity wallets, verifiable credentials, and self-sovereign identity revolutionize secure, user-centered digital trust in a rapidly evolving digital landscape.

What’s in a Name - A Case for Verifiable Credentials
Outdated identification methods can cause serious errors in industries like travel and healthcare. Verifiable credentials offer a secure solution by ensuring unique, precise identity verification.

Best Practices for Remote Identity Proofing in Healthcare
Discover essential best practices for remote identity proofing in healthcare to protect patient data, ensure compliance, and build trust with secure, user-friendly verification methods.
Who’s Really Making Healthcare Decisions? The Hidden Dangers of Not Verifying Proxies
Learn how identity proofing protects patient privacy, prevents fraud, ensures trust, and complies with regulations for healthcare proxies in today's healthcare landscape.

Securing Telehealth: Why Identity Proofing is More Than Just a Good Idea
Identity proofing is essential for secure telehealth, protecting patient data, ensuring compliance with regulations, and enhancing trust and experience. Learn key IAM best practices.

The Critical Need for Modern Identity Proofing in Healthcare
Modern identity proofing is essential in healthcare to protect patient data, ensure regulatory compliance, and enhance overall patient experience amid increasing digital transformation.

The Growing Threat of Deepfakes to Remote Identity Verification
Learn how advanced biometric solutions and regulatory measures can protect against the rising threat of deepfakes in remote identity verification systems.

The Importance of Just-in-Time Access in Privileged Access Management
Discover the significance of Just-in-Time Access in Privileged Access Management. Learn how JIT access enhances security, reduces attack surfaces, ensures compliance, and boosts operational efficiency in today's cyber threat landscape.

Enhancing Security with Zero Standing Privileges and Identity Governance
Enhance security with Zero Standing Privileges and Identity Governance, exploring the relationship between the two concepts and how their integration can bolster access management and enhance security measures in a digital landscape.

The Power of Bring Your Own Identity (BYOI)
Explore the concept of Bring Your Own Identity (BYOI) and its impact on personalization, convenience, and privacy in the digital realm. Discover how BYOI revolutionizes identity management and empowers individuals online.
In Pursuit of Trust: Exceeding Expectations in Project Delivery
Discover the importance of exceeding expectations in project delivery and the impact of dedication on building trust with partners and clients.

How do you Implement IAM? One Bite at a Time
Implementing IAM can be overwhelming, but breaking it down into manageable phases is the key. This blog explores the five stages of IAM implementation and highlights the importance of a gradual approach. Discover how to analyze, architect, implement, test, and support IAM solutions effectively.

Designing for Resiliency
Avoid outages by building highly redundant and scalable identity and access management solutions.
Identity Fusion Responds to Directory Services (OpenDJ) Security Advisory #201703
ForgeRock released Security Advisory #201703 covering two medium security vulnerabilities for Directory Services (OpenDJ) impacting versions 2.6 on up to 3.5.1 as well as the embedded OpenDJ in OpenAM 12.X, 13.0.0, and 13.5.0. Vulnerability Issue #201703-01: Bind Request trace logging shows plaintext password The first vulnerability “Bind Request trace logging shows plaintext password”, is only Read more
OpenIDM Property Value Substitution
Property value substitution can be a useful technique for customizing OpenIDM deployments across multiple environments. Assume, for instance, that you have three environments (Development, Test, and Production). Your OpenIDM deployment has been configured for one OpenDJ system resource, but the configuration properties for that resource is different across each environment. The following diagram demonstrates the Read more

Configuring OpenIDM Password Reset
ForgeRock OpenIDM is a powerful account management and data synchronization tool that provides many robust features out of the box. Some of these features must be enabled, however, before they can be used. Once such feature allows a user to reset their password in the OpenIDM Web UI by responding to challenge questions. The OpenIDM Read more
OpenDJ and the Fine Art of Impersonation
Directory servers are often used in multi-tier applications to store user profiles, preferences, or other information useful to the application. Oftentimes the web application includes an administrative console to assist in the management of that data; allowing operations such as user creation or password reset. Multi-tier environments pose a challenge, however, as it is difficult Read more
Hacking OpenAM – An Open Response to Radovan Semancik
I have been working with Sun, Oracle and ForgeRock products for some time now and am always looking for new and interesting topics that pertain to theirs and other open source identity products. When Google alerted me to the following blog posting, I just couldn’t resist: Hacking OpenAM, Level: Nightmare Radovan Semancik | February 25, 2015 There Read more
OpenDJ Access Control Explained
An OpenDJ implementation will contain certain data that you would like to explicitly grant or deny access to. Personally identifiable information (PII) such as a user’s home telephone number, their address, birth date, or simply their email address might be required by certain team members or applications, but it might be a good idea to Read more

The Next Generation of Identity Management
The face of identity is changing. Historically, it was the duty of an identity management solution to manage and control an individual’s access to corporate resources. Such solutions worked well as long as the identity was safe behind the corporate firewall – and the resources were owned by the organization. But in today’s world of Read more

OpenIDM 3.1: A Wake Up Call for Other Identity Vendors
Having implemented Sun, Novell, and Oracle provisioning solutions in the past, the one thing that I found to be lacking in ForgeRock’s OpenIDM solution was an easy to use administrative interface for connecting to and configuring target resources. Sure, you could configure JSON objects at the file level, but who wants to do that when Read more
OpenDJ Attribute Uniqueness (and the Effects on OpenAM)
In real life we tend to value those traits that make us unique from others; but in an identity management deployment uniqueness is essential to the authentication process and should not be taken for granted. Case in point, attributes in OpenDJ may share values that you may or may not want (or need) to be unique. For Read more
Understanding OpenAM and OpenDJ Account Lockout Behaviors
The OpenAM Authentication Service can be configured to lock a user’s account after a defined number of log in attempts has failed. Account Lockout is disabled by default, but when configured properly, this feature can be useful in fending off brute force attacks against OpenAM login screens. If your OpenAM environment includes an LDAP server Read more
It’s OK to Get Stressed Out with OpenAM
In fact, it’s HIGHLY recommended…. Performance testing and stress testing are closely related and are essential tasks in any OpenAM deployment. When conducting performance testing, you are trying to determine how well your system performs when subjected to a particular load. A primary goal of performance testing is to determine whether the system that you Read more

Understanding the iPlanetDirectoryPro Cookie
So you have run into problems with OpenAM and you are now looking at the interaction between the Browser and the OpenAM server. To assist you in your efforts you are using a plug-in like LiveHttpHeaders, SAML Tracer, or Fiddler and while you are intently studying “the dance” (as I like to call it), you Read more

How to Configure OpenAM Signing Keys
The exchange of SAML assertions between an Identity Provider (IdP) and a Service Provider (SP) uses Public-key Cryptography to validate the identity of the IdP and the integrity of the assertion. Securing SAML Assertions SAML assertions passed over the public Internet will include a digital signature signed by an Identity Provider’s private key. Additionally, Read more
OpenDJ Indexes Explained
Suppose that you have an OpenDJ directory server with 300,000 entries. And further suppose that the space consumed on your disk for said directory is 1.2 GB and made up of 114 database (*.jdb) files. Suppose that you didn’t plan correctly and you are now running out of space on your hard drive. What should Read more
The Case of the Mysteriously Creeping Database
While teaching a recent ForgeRock OpenDJ class, a student of mine observed an interesting behavior that at first seemed quite odd. While rebuilding his attribute indexes, the student found that the overall database size seemed to grow each time he performed a reindex operation. What seems obvious to me now sure made me scratch my head Read more
What do OpenDJ and McDonald’s Have in Common?
The OpenDJ directory server is highly scalable and can process all sorts of requests from different types of clients over various protocols. The following diagram provides an overview of how OpenDJ processes these requests. (See The OpenDJ Architecture for a more detailed description of each component.) Note: The following information has been taken from ForgeRock’s OpenDJ Administration, Read more

The Dimishing Non-Digital World (or How to get Outed by a Photo Booth)
I recently attended a high school reunion where a major draw involved the use of a photo booth. You remember photo booths, right? Kiosks where one or more people hide behind a curtain and take pictures of themselves in all sorts of poses. At the end of the session, the kiosk spits out copies of Read more
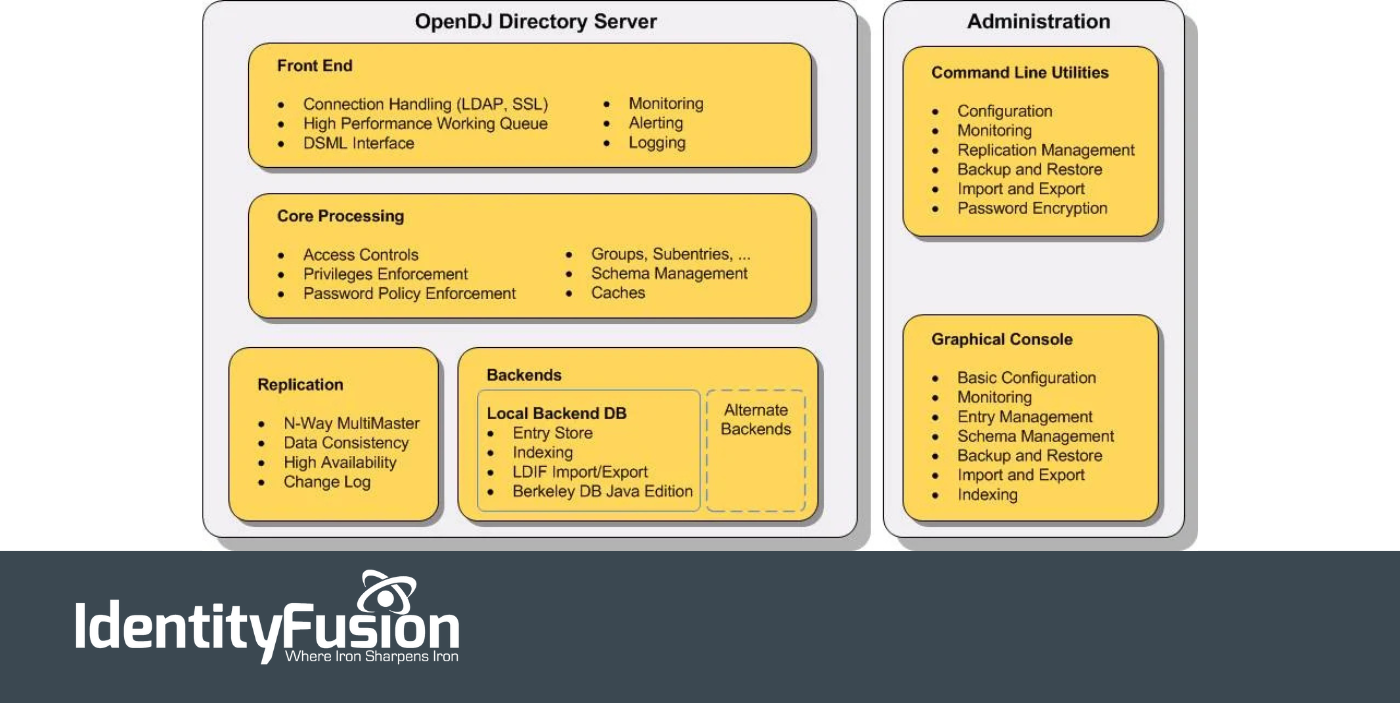
The OpenDJ Architecture
An understanding of the components that make up the OpenDJ Architecture is useful for administering, configuring, or troubleshooting the OpenDJ server. The following information has been taken from ForgeRock’s OpenDJ Administration, Maintenance and Tuning Class and has been used with the permission of ForgeRock. The OpenDJ server has been developed using a modular architecture in which most Read more

A New Generation of Indentured Servitude
Your digital identity is comprised of information that you volunteer about yourself and information that is observed about you as you simply participate in life. You can (somewhat) control the personal data that you share with others, but have you ever wondered about the type of information that is gathered about you, how long it Read more
Unlocking the Mystery behind the OpenDJ User Database
One question that arises time and time again pertains to the manner in which OpenDJ stores it entry data and how this differs from the Oracle Directory Server Enterprise Edition (previously known as Sun Directory Server Enterprise Edition). The following information is from ForgeRock’s OpenDJ Administration, Maintenance and Tuning Class and has been used with the Read more

How Well Do Your Vendors Really Know You?
How well do our vendors know us? I mean, how well do they really know us? And how much do they care? They collect countless data points about us through direct or indirect activity. They spend a lot of money buying lists containing all sorts of information about “people like us”, but what are they actually Read more
The Most Complete History of Directory Services You Will Ever Find
I started working with Directory Servers back in 1997 when Netscape was but a fledging company. Over the past 15 years a lot has changed. Companies have come and gone and code has changed hands more times than I care to remember. But one thing remains the same – that little effort started by Tim Howes, Read more

Trust in Me
Trust in me, I’m the social media vendor providing this FREE service because I want to make you happy. I know that all of this infrastructure and the thousands of employees I have working for me are costing a small fortune, but I do this because I care …. I care about YOU! Trust in me, Read more

The Road Back to Eden
We oftentimes view new technologies as providing us with the path back to Eden – that which returns us to leisure and care free living. Yet with each new technological improvement, our lives do not become easier, they are simply changed. The widespread availability of electricity and electric appliances in the early 1900s, promised to transform the Read more

Facebook Photo Hack Bypasses Privacy Settings
Do you use Facebook? Since over 700 million people do, the odds are pretty high that you fall in this category. Are you concerned with your privacy and want control over who sees your content? Have you taken all the steps necessary to keep your private information private and feel pretty good about yourself? Well Read more

Disjointed Identity
Having my identity located in so many different databases is like wearing multiple watches You never really know what time it is!

Single Sign-On Explained
Single-Sign-On reduces the number of times you must enter a username and password. Explore Enterprise Single Sign-On (ESSO) & Web Single Sign-On (WSSO).

Dealing with Grief in a Social Setting
We had to put our family dog down. Princess Buttercup of Petersburg was my daughter’s first real pet and as my daughter grew so did Buttercup. For the past twelve years we celebrated life’s events and Buttercup was right there with us, every step of the way. Birthdays, holidays, even more pets; we could look Read more

The Biggest Expense to Your Company
While reading the book, I’m Feeling Lucky: The Confessions of Google Employee Number 59, I stumbled on a question that Sergey Brin asked of his marketing folks. It really got me to think about how we look at corporate costs. Think for a second, what is the biggest expense that a company can incur? Is Read more

Trust – The Missing Ingredient
I was having a conversation with friends the other day and while it may sound nerdy as hell, the topic was focused on identity. I swear (trust me) that no drinks were involved but the conversation went pretty deep, nonetheless. What is identity, how is it used, and how can it be protected? Like Aristotle Read more

Facebook’s Trolling for Keywords
I posted a status to Facebook that included the words “Sea World” and all of a sudden I received a recommended page for Sea World and other Orlando theme parks in their advertisement section. Does anyone really think that Facebook isn’t parsing every post for nuggets they can glean and use for advertising purposes? From Read more

Is Your Intellectual Property Slipping Out the Door with Their Pink Slip?
(I wrote the following article for BABM Business Magazine back in May/June of 2009. The article is reprinted here with their permission.) With the latest layoff news continuing to add chaos to the economy, CEOs need to protect their businesses in case of staff cuts, restructuring or consolidation of offices. While your company may not Read more

Advice to CIOs for High Exposure Projects
Opinion on a CIO Magazine about the plight of today’s CIOs when multi-million dollar multi-year projects go awry.

Opinions About the Federal Government’s Identity Initiative
Interesting read. This is essentially a WebSSO initiative with authentication based on CAC type ID cards or OpenID. The CAC type of implementation (ID Cards) are not practical as they require everyone to have a card reader on their PC in order to do business with the government. I don’t see this happening anytime too Read more

Book Review: Digital Identity
Digital Identity by Phillip J. Windley See this book on Amazon » Bill has read this book Recommend This is a clear, consise, and easy to read book on IDM and DRM. I recommend it HIGHLY to anyone who wants an overview of IDM and its roots in the X.500 space. While Digital Identity does Read more

Identity Management Lessons from Sarah Palin
By now, many of you have already heard about the hacking of Alaska Governor Sarah Palin’s Yahoo e-mail account earlier this week (on or about Tuesday 9/16/2008). If not, here is a brief synopsys of the story. Sarah Palin’s personal Yahoo e-mail account was compromised and the contents of her account (including her address book, Read more
Directory Servers vs Relational Databases
An interesting question was posed on LinkedIn that asked, “If you were the architect of LinkedIn, MySpace, Facebook or other social networking sites and wanted to model the relationships amongst users and had to use LDAP, what would the schema look like?” You can find the original post and responses here. After reading the responses Read more